
Ransomware statistics from the FBI show 3,611 complaints in 2025, up from 3,156 in 2024, with the reported total likely well below the real number. More than 1,400 of those complaints came from businesses outside critical infrastructure, led by law firms and contractors. This guide covers the figures, who is being hit, and how backups change the outcome.
Last reviewed: October 6, 2026. This is general information, not security advice.
Key takeaways
- The FBI IC3 received 3,611 ransomware complaints in 2025, up about 14% from 3,156 in 2024.
- Reported ransomware losses were about $32.3 million, a figure IC3 says is artificially low.
- More than 1,400 complaints came from non-critical-sector businesses, led by legal services (18%) and contracting (17%).
- The ten most active variants in 2025 included Akira, Qilin and INC/Lynx/Sinobi.
- A tested offsite backup is the control that most changes what a ransomware attack costs.
Ransomware complaints by year
The FBI’s 2025 Internet Crime Report counted 3,611 ransomware complaints. Figure 1 puts that next to the earlier reports. The series rose to 3,729 in 2021, fell to 2,385 in 2022 and has climbed in each year since then.
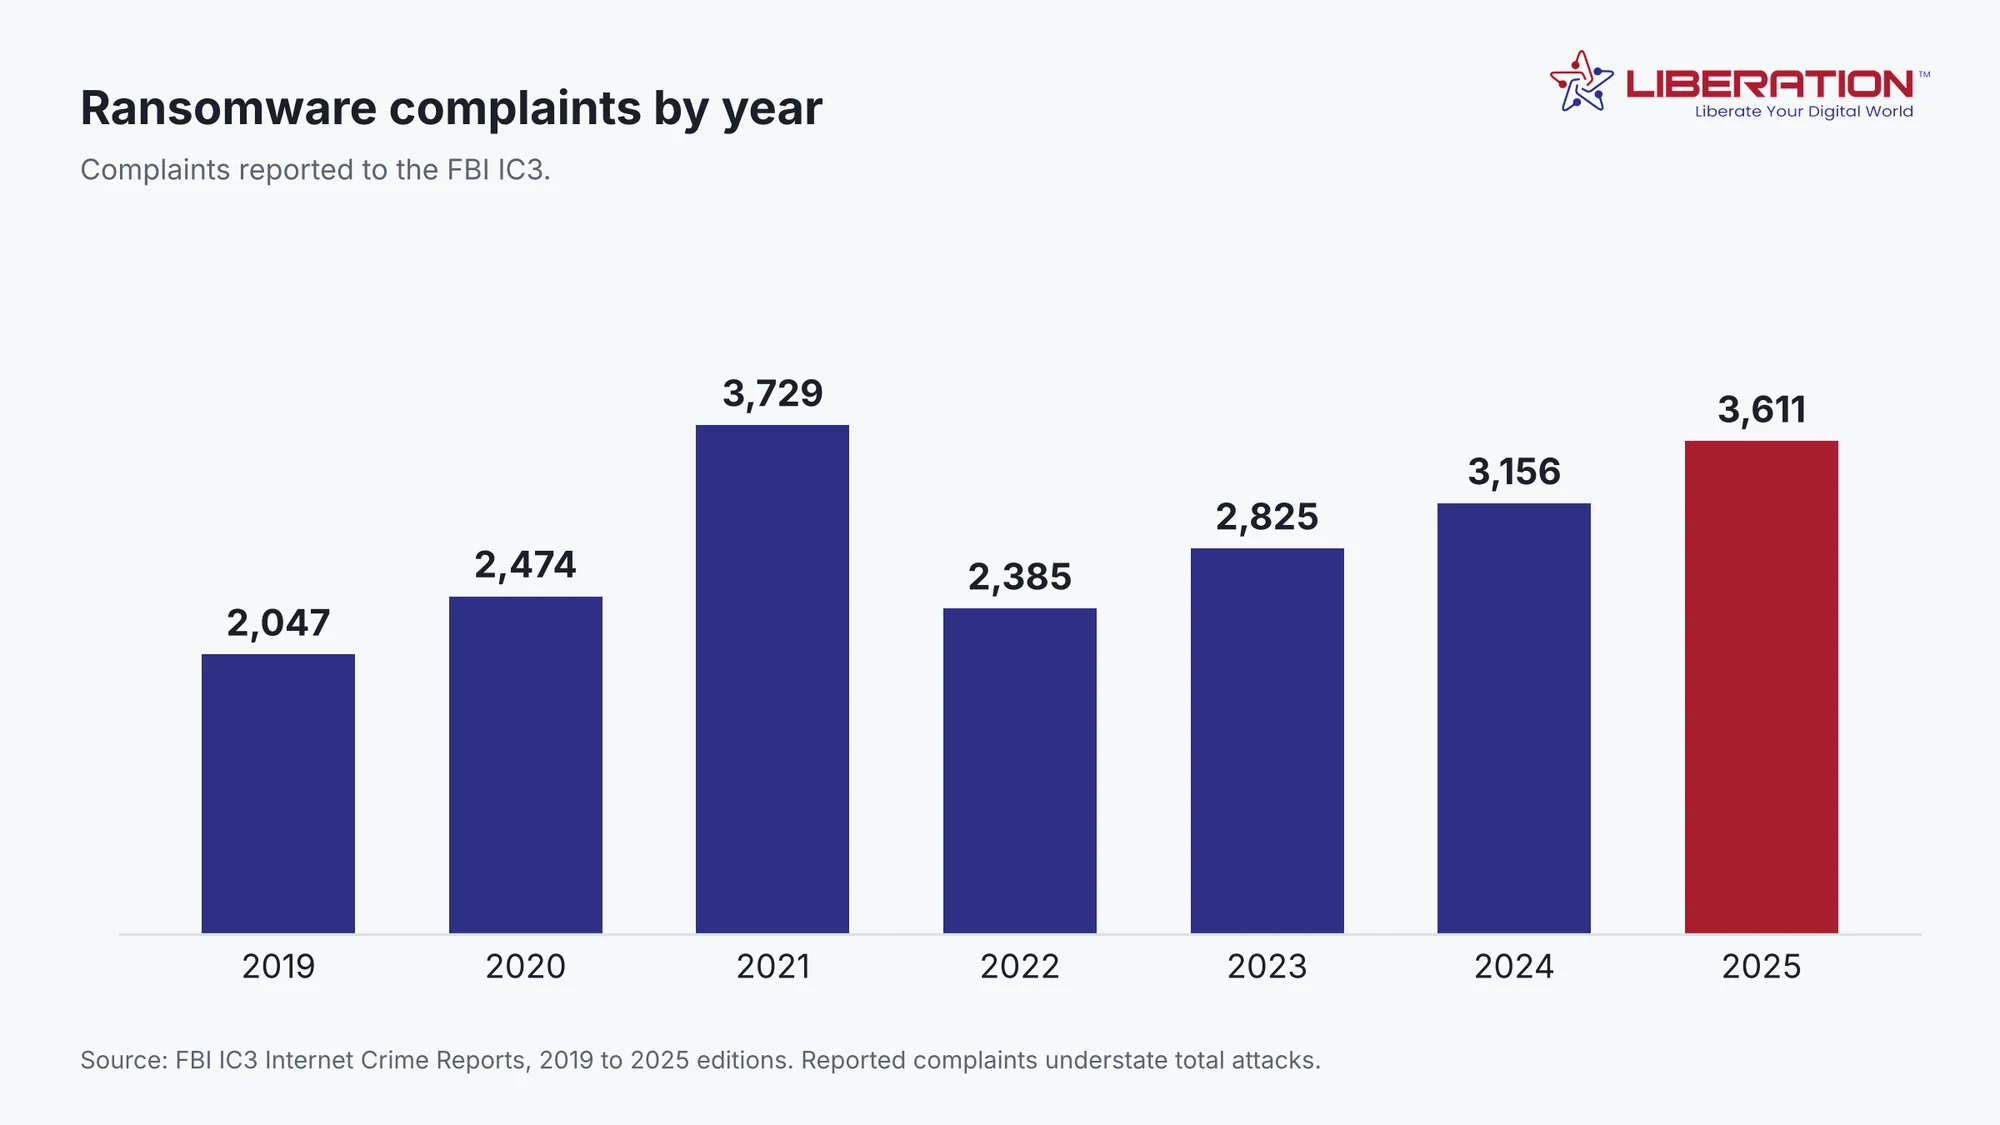
These are victim reports, so they are a floor. The dollar figures are even less complete. IC3 recorded about $32.3 million in reported ransomware losses for 2025 and states that the number leaves out lost business, remediation costs and many cases where victims gave no amount. The loss figure fell to about $12.5 million in 2024 and rose to $32.3 million in 2025, which shows how unevenly victims report it. Do not use it as a measure of the cost of an attack.
Who is being hit
The report’s critical infrastructure sections focus on manufacturing, healthcare and government facilities. A less-noticed section covers businesses outside those sectors, which accounted for more than 1,400 of the 2025 ransomware complaints. Figure 2 shows the leading industries.
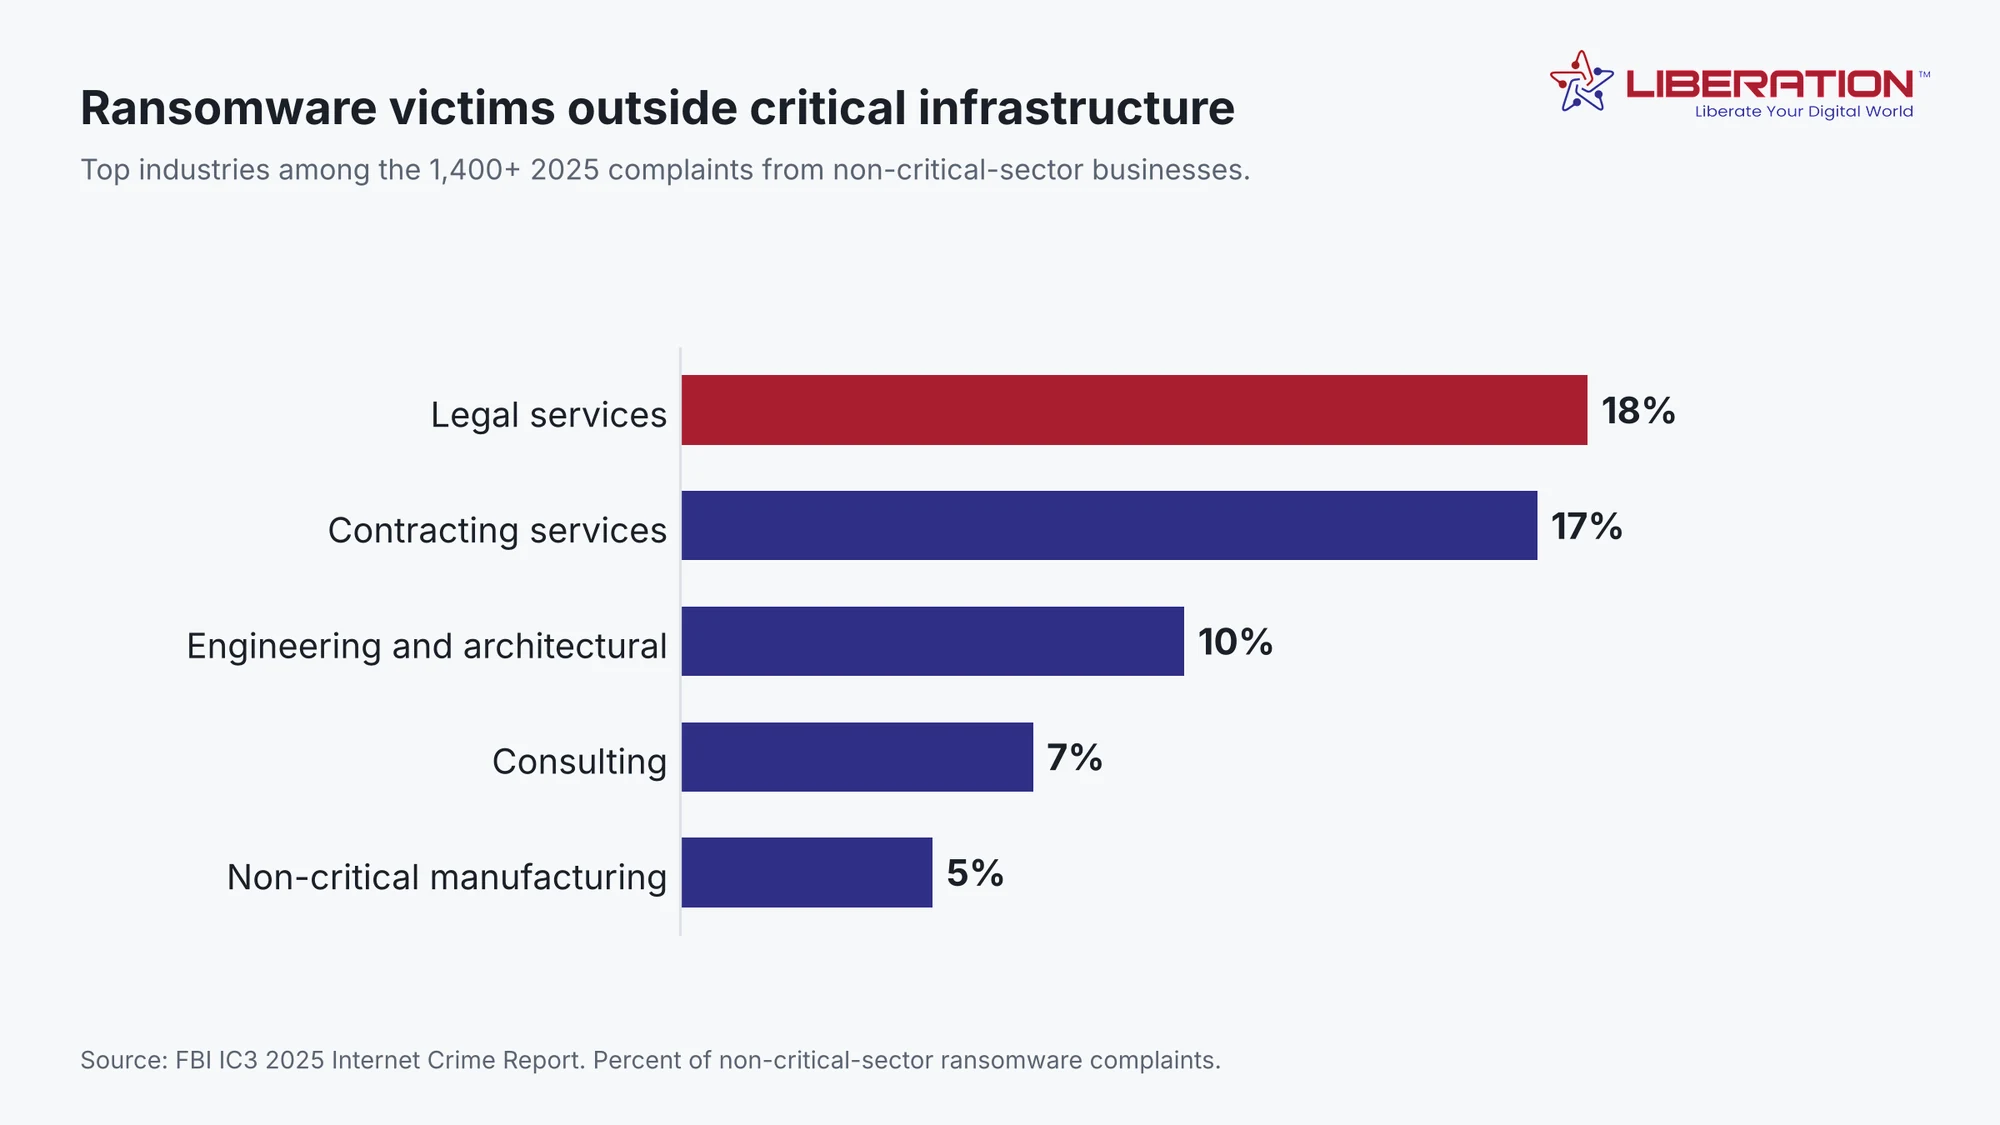
Legal services, contractors, engineering firms and consultancies share a profile. They are small and mid-size firms that hold client money, drawings or confidential files, and many do not have a dedicated security team. Firms like these are poorly placed to absorb a week offline.
What this means for a small business
A ransomware attack has two costs. One is the ransom, which not every victim pays. The other is the downtime, which every victim pays. A business with a recent, clean backup can restore its systems and skip the ransom decision. Without one, the choice is between paying and losing the data. The controls below address the common routes in.
| Common route in | Control |
|---|---|
| Phishing email with a malicious attachment or link | Filtering, multi-factor authentication and staff training |
| Unpatched server or website software | Scheduled updates and monitoring for known vulnerabilities |
| Exposed remote access | Multi-factor authentication, restricted access and logging |
| Backups reachable from the infected network | Offsite or immutable backups, and a tested restore plan |
Four steps that change the outcome
1. Keep backups out of the attacker’s reach
Ransomware often searches for and encrypts backups connected to the network. Keep at least one copy off site or immutable. Our backup and disaster recovery service can help with this.
2. Test the restore
Restore a set of files and a full system to a test machine at least once a year, and record how long it takes. That time is your real recovery time.
3. Protect the website too
A compromised site can host malware or lose its data. Automated website backups with CodeGuard keep a clean copy of your files and database.
4. Close the common doors
Turn on multi-factor authentication, patch on a schedule, and remove remote access you do not need.
Frequently asked questions about ransomware statistics
How many ransomware attacks are reported each year?
The FBI IC3 received 3,611 ransomware complaints in 2025, up from 3,156 in 2024. The 2021 peak in the series was 3,729. Many attacks go unreported, so real counts are higher.
How much do ransomware victims lose?
IC3 recorded about $32.3 million in reported ransomware losses for 2025, but the agency warns that the number is artificially low. It excludes lost business, remediation costs and the many cases where victims report no loss amount.
Do small businesses get hit by ransomware?
Yes. IC3 reports that more than 1,400 of the 2025 ransomware complaints came from businesses outside the critical infrastructure sectors, led by legal services (18%) and contracting services (17%).
Which ransomware groups were most active in 2025?
IC3 listed Akira, Qilin, INC/Lynx/Sinobi, BianLian, Play, Ransomhub, Lockbit, Dragonforce, SAFEPAY and Medusa as the top 10 variants in 2025 complaints.
What is the best protection against ransomware?
Tested offsite backups that an attacker cannot reach from your network, multi-factor authentication, prompt patching, and limits on administrator access. Backups turn a ransom demand into a restore job.